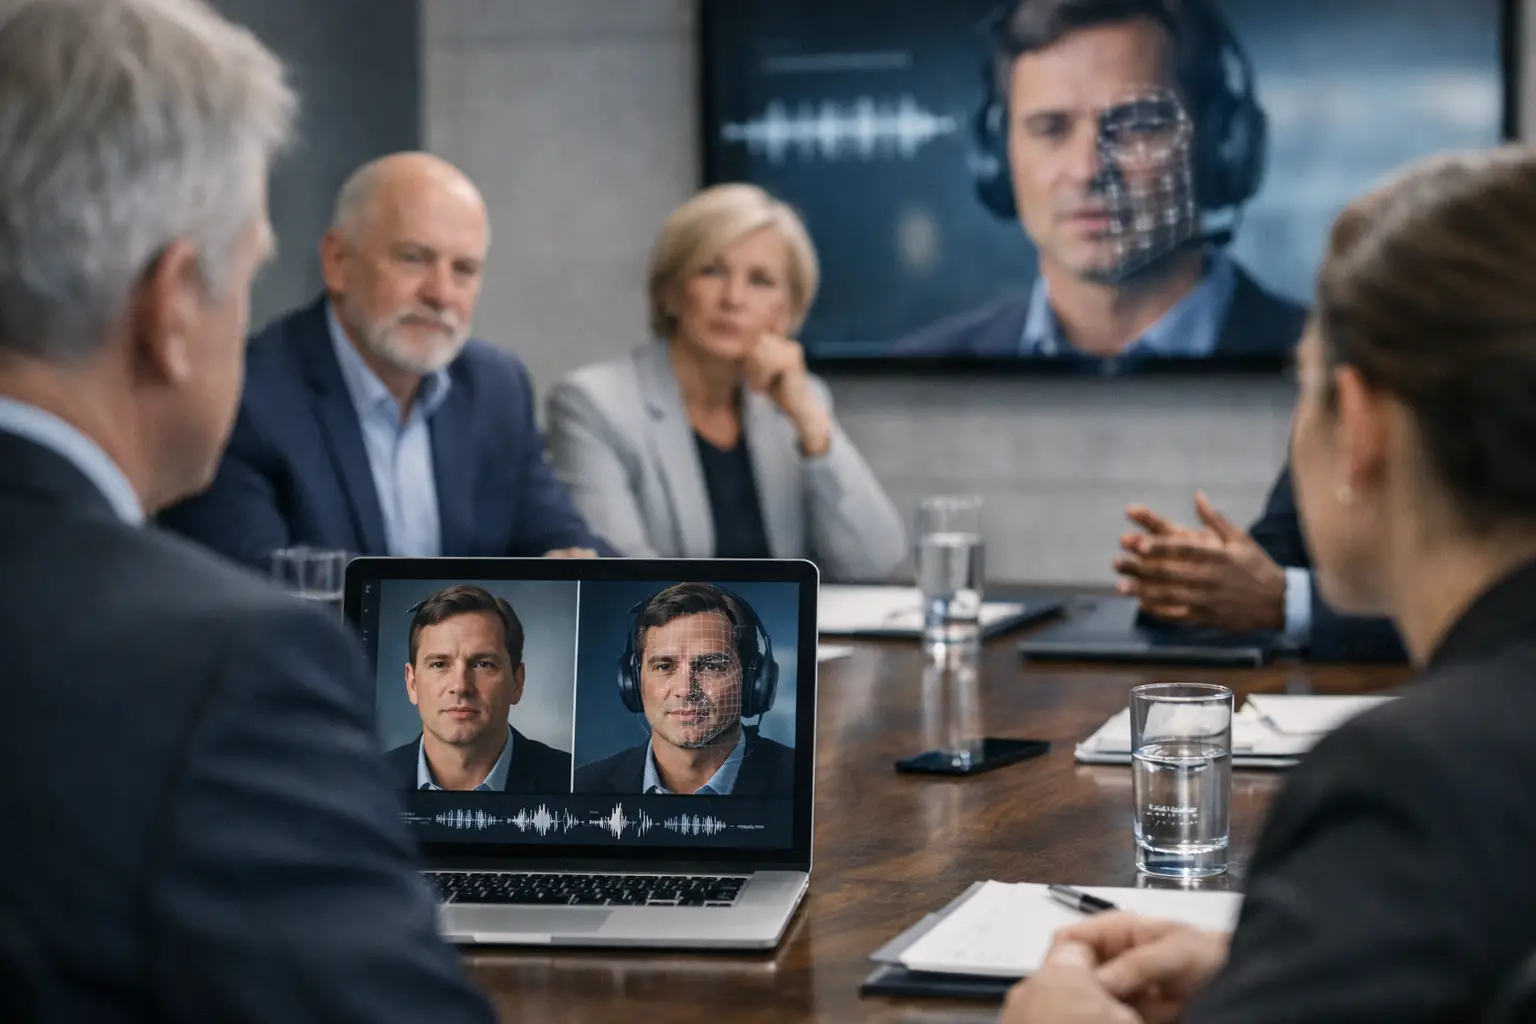
A finance director receives a WhatsApp voice message from the CEO: a supplier payment needs to clear before close of business. The voice is right. The urgency is familiar. The payment details are new. This is where deepfake fraud questions stop being a cyber awareness exercise and become an operational control issue.
For Australian organisations, the central risk is not simply a convincing fake video on social media. It is the use of synthetic voice, video, images and written communication to defeat the human checks surrounding money movement, privileged access, customer identity and sensitive information. Attackers do not need perfection. They need one rushed employee, an unclear approval path or a team that treats a familiar face or voice as proof.
1. Which business processes rely on a voice, face or message as proof?
Start with the uncomfortable question: where does your organisation accept human familiarity in place of verification? Senior executives are routinely impersonated because their authority can shorten conversations and bypass normal caution. Finance, payroll, IT service desks, legal teams and executive assistants are common targets.
Map the workflows where a request can trigger a high-impact action. This includes changing supplier bank details, approving urgent payments, releasing payroll data, resetting multi-factor authentication, creating privileged accounts, sharing customer records or altering invoice instructions.
The key distinction is between identification and authentication. A staff member may identify a caller as their manager because the voice sounds correct. That does not authenticate the request. A process that treats recognition as verification is vulnerable by design.
2. What must happen before money, access or data can move?
Deepfake fraud succeeds when a verbal request becomes an executable instruction without an independent check. The remedy is not telling people to be more suspicious. It is defining a mandatory verification step that cannot be controlled by the same fraudulent communication channel.
For payment changes, require a call-back to a trusted number already held in your records, not the number supplied in the request. For privileged access resets, require a separate identity verification method and a second authorised approver. For sensitive data requests, enforce documented approval through an established workflow rather than email or messaging alone.
This can create friction. That is the trade-off. But a two-minute control is considerably cheaper than recovering a misdirected payment or explaining a data breach to customers, regulators and insurers. The aim is targeted friction around irreversible actions, not slowing every ordinary interaction.
3. Can an attacker exploit an exception path?
Most teams know the standard process. Fraudsters target the exceptions: the executive travelling overseas, the supplier whose details “must” change today, the after-hours incident, the employee who has lost their mobile, or the urgent acquisition matter that cannot be discussed widely.
Ask whether the control still works when seniority, urgency or confidentiality are invoked. If an executive can override payment controls by sending a voice note, the control is optional. If a service desk can reset access after a video call, then the service desk has effectively become an identity assurance function without the tools or authority to perform it.
Exception paths should be defined in advance. They need clear escalation owners, recorded approvals and a verification method that is resistant to impersonation. “Use judgement” is not a control when the request appears to come from the CEO.
4. Are our people trained on the right deepfake fraud questions?
Generic phishing training is no longer enough. Employees need practical prompts that match their role and the decisions they make. A finance team member should know that a familiar executive voice does not validate changed bank details. An IT administrator should know that a convincing video call does not replace approved identity verification. A customer-facing team should understand the signs of account takeover enabled by fabricated identity documents or live video.
Train teams to pause and ask: is this request asking me to bypass a known process? Is the urgency preventing independent verification? Has the request changed details that should be stable? Can I confirm it through a separate trusted channel?
Avoid turning this into a one-off compliance module. Use short scenario-based exercises within finance, IT, HR and executive support functions. Measure whether staff follow the escalation process, not whether they can define a deepfake.
5. Where are our detection blind spots?
Human verification controls are the first line of defence, but they do not answer every risk. Organisations also need to understand where synthetic media could enter their environment and what evidence is retained when it does.
Consider recruitment and onboarding, customer verification, remote support, executive communications, fraud investigations and third-party access. A fabricated identity could be used to secure a role, gain access to systems or establish a fraudulent customer account. A cloned voice could be used against a help desk. A manipulated video could be used to pressure a commercial partner or damage a brand.
Detection technology can assist by analysing audio, video and image content for signs of manipulation. It is useful where media authenticity has material consequences, particularly at scale. It is not a licence to remove process controls. Detection systems can produce false positives and false negatives, while attackers continue to improve. Use them as part of a layered decision process, with clear escalation and evidence handling.
6. Do our suppliers and partners have the same verification discipline?
Your controls can be sound while your supply chain remains exposed. A compromised or impersonated supplier may send a legitimate-looking invoice change. A partner may receive a fake instruction that appears to come from your executive team. A managed service provider may be asked to make an urgent access change on your behalf.
Set expectations contractually and operationally. Confirm how banking changes are verified, how service providers handle urgent access requests, who may authorise changes, and which communication channels are accepted for high-risk instructions. Maintain current contact details for critical suppliers and establish a known escalation route before an incident occurs.
For larger organisations, this should be part of third-party risk management. For smaller businesses, a concise supplier verification procedure can still close the most obvious gap. Scale the control to the risk, but do not assume a familiar supplier relationship is immune to impersonation.
7. Can we investigate and contain an incident quickly?
When a suspected deepfake is reported, time matters. The first goal is containment: halt the payment, suspend the access change, preserve the message and alert the appropriate owners. The second is evidence: retain emails, chat logs, audio files, call records, account activity and approval history. The third is recovery: identify what moved, who was exposed and whether the attacker has an ongoing foothold.
A usable response plan assigns roles before the incident. Finance owns payment recalls and banking engagement. IT and security investigate account activity and contain access. Legal, risk and communications assess reporting obligations and stakeholder impacts. Executive leadership decides on material business actions. Without this division of responsibility, teams lose valuable time debating ownership while the attacker moves on.
Test the plan against a realistic scenario. For example, a synthetic voice request leads to a supplier payment change, followed by a request to reset an approver's multi-factor authentication. This tests the crossover between financial controls, identity controls and incident response - precisely where deepfake-enabled fraud is likely to create pressure.
A control problem, not a novelty problem
Deepfakes are not dangerous because they are technically impressive. They are dangerous because many business processes still trust familiar signals over independently verified facts. The right response is disciplined: identify high-impact workflows, separate communication from verification, enforce approval rules, train teams on realistic scenarios and test response paths.
Technow can help security and technology leaders assess identity, communication and fraud controls against this emerging threat. Book a Discovery Call to identify where a synthetic identity could currently move money, access or data through your business.